CodeDebrief: Local MCP server that maps code for AI agents
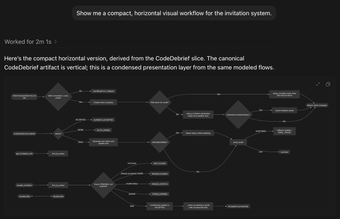
CodeDebrief, by Ferdinandobons, is an MCP server and static analysis tool that converts codebases into navigable workflow maps to ground AI agents' understanding. It performs on-repo analysis and emits Mermaid flowcharts and MCP-accessible artifacts so agents can reference repository structure and control flow. The tool targets software engineers using AI coding assistants who need source-grounded context for code review, onboarding, and question-answering in complex projects and produces artifacts agents can query during developer workflows.
What tasks can you actually use it for?
The tool serves AI coding agents by exposing repository structure and control flow through the Model Context Protocol, letting agents query code-aware artifacts during developer work. Integration is possible with MCP-compatible hosts such as Claude Desktop and GitHub Copilot. Typical tasks include orienting an agent to unfamiliar modules, answering logic-based questions, and assisting code review and onboarding workflows where a deterministic view of implementation paths improves agent relevance.
How accurate are the outputs compared to LLM summaries?
Rather than generating probabilistic text summaries, the tool uses static analysis to produce deterministic, source-grounded artifacts that reflect concrete control flow. This approach reduces reliance on surface-level language patterns and helps agents reference actual code logic. The visual artifacts and maps are designed to be verifiable against the repository, which supports decision-making in debugging and design discussions where traceable origins of an answer matter more than paraphrased explanations.
What inputs and environments does the tool require?
The tool runs as a Node.js and Python server and is compatible with any host that implements the Model Context Protocol, according to its documentation. The analyzer supports multiple programming languages including C++ and Python, and the analyzer, artifacts, and MCP server are designed so no LLM provider key is required for the analysis phase. Deployment therefore needs an MCP-capable environment rather than a particular cloud service.
Does it require significant setup or security review?
The tool packages nine specialized utilities for code comprehension and navigation, which helps bridge agent gaps across large systems. As an independent developer project, the developer focuses on MCP tooling for agents. Security platforms assigned a Risk Grade B to the project, indicating a defined toolset that merits standard review before deployment with sensitive repositories. Teams should plan for server setup and artifact vetting as part of adoption.
A focused, community-oriented choice for MCP ecosystem engineers
CodeDebrief is a solid fit for software engineers working within the MCP ecosystem who need agent-aware tooling and are willing to perform local deployment and security checks. The project's recognition in the MCP community supports its suitability, while a Risk Grade B rating recommends a standard security review before use on sensitive repositories. Teams with operations capacity will extract the most value.